Data Security & Governance
Protect Data Wherever It Resides or Moves
Enterprise information now moves between public clouds, SaaS applications, corporate endpoints, employees, partners and AI services. Sensitive data can be exposed through excessive permissions, insecure configurations, inappropriate sharing or everyday user activity. Securing a network connection alone does not establish whether the information being accessed or transferred should be available to that user.
Hararei helps organizations establish a coordinated data security strategy using Zscaler technologies. We combine data discovery and classification, data security posture management (DSPM), data loss prevention (DLP) and SaaS security with practical policy design and ongoing operations. The objective is to understand what needs protection, reduce unnecessary exposure and apply appropriate controls without obstructing legitimate business activity.
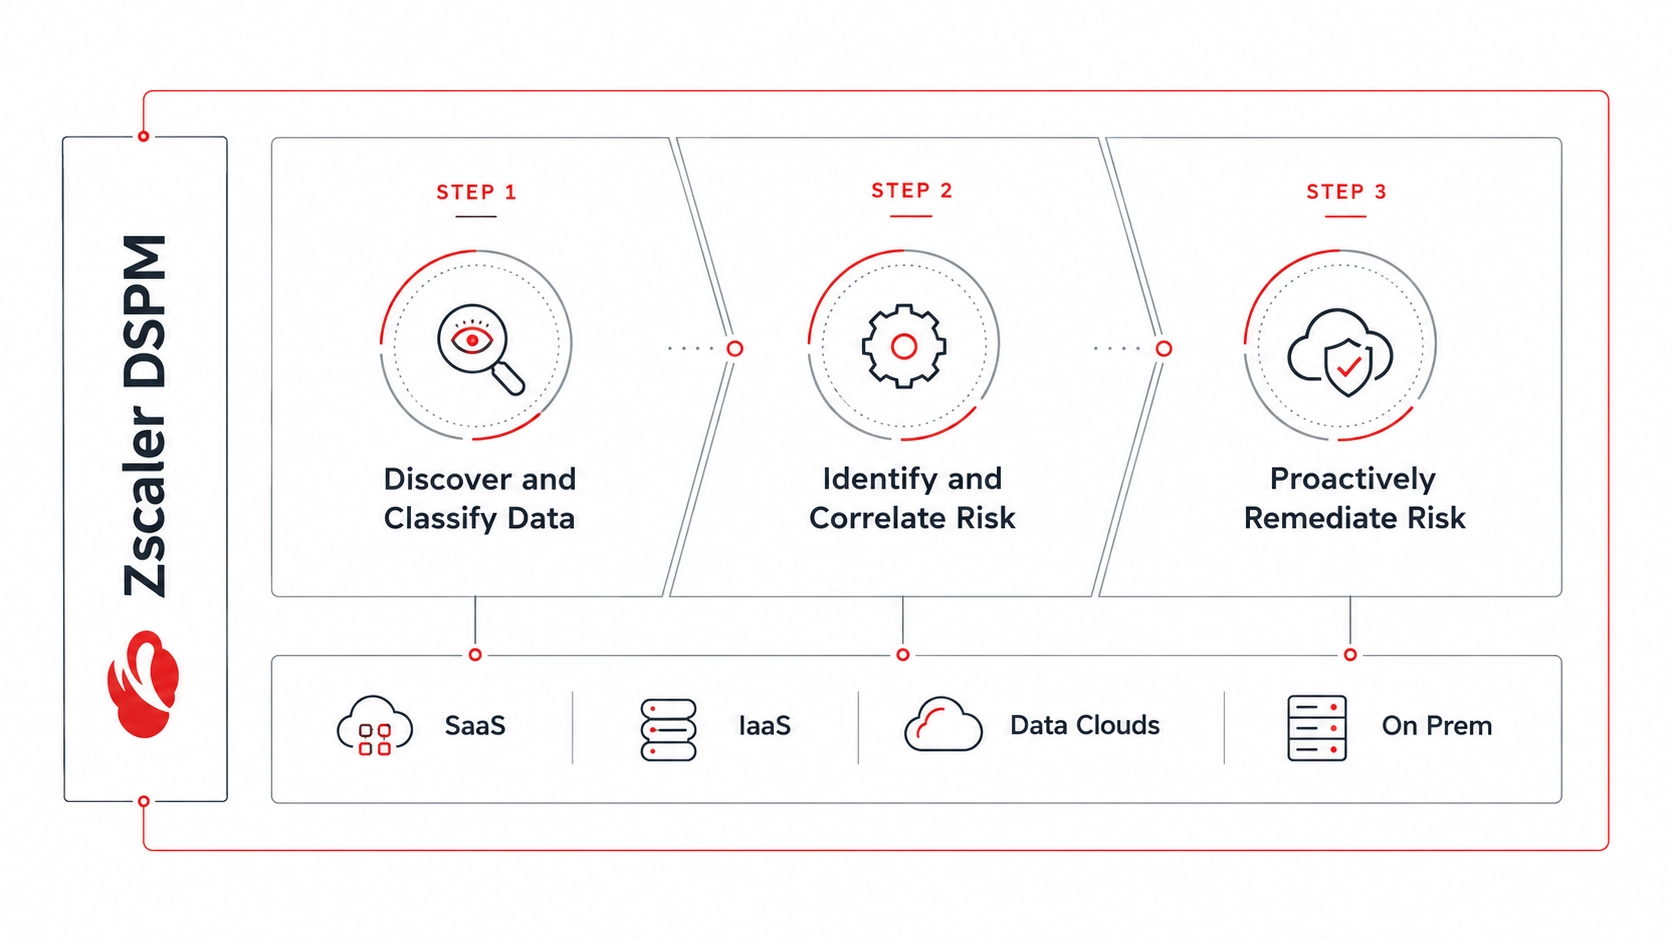
Data Security Posture Management
Why Traditional Data Protection Is No Longer Enough
Incomplete Data Visibility
Sensitive information may be distributed across cloud storage, databases and collaboration platforms without consistent discovery or classification.
Excessive Access
Broad permissions, external sharing and misconfigured resources can expose information even when no deliberate data transfer takes place.
Fragmented Enforcement
Separate tools and policies for web traffic, SaaS, endpoints and cloud data can create gaps, inconsistent decisions and additional administrative effort.
A Coordinated Approach to Data Security
Effective data security requires two complementary capabilities: understanding and reducing the exposure of data at rest, and controlling how sensitive information is used and transferred. Hararei designs these capabilities to work together rather than treating discovery, posture and DLP as independent projects.
Discover & Classify
Locate sensitive information in supported environments, identify relevant data types and establish a consistent basis for protection policies.
Understand Exposure
Review where sensitive data is stored, who can access it, and which permissions or configurations increase risk.
Enforce Data Controls
Apply classification-aware policies to relevant data movement and sharing channels, with actions appropriate to the sensitivity and business context.
Monitor & Improve
Investigate incidents, address recurring causes of exposure and refine policies as business processes, applications and data locations change.
Data Security Posture Management: Reduce Exposure Before Data Moves
Data security posture management focuses on sensitive information already stored in the enterprise environment. Using Zscaler DSPM, Hararei helps organizations discover and classify supported data stores, understand data access and identify risks such as excessive permissions, unnecessary exposure and configuration weaknesses.
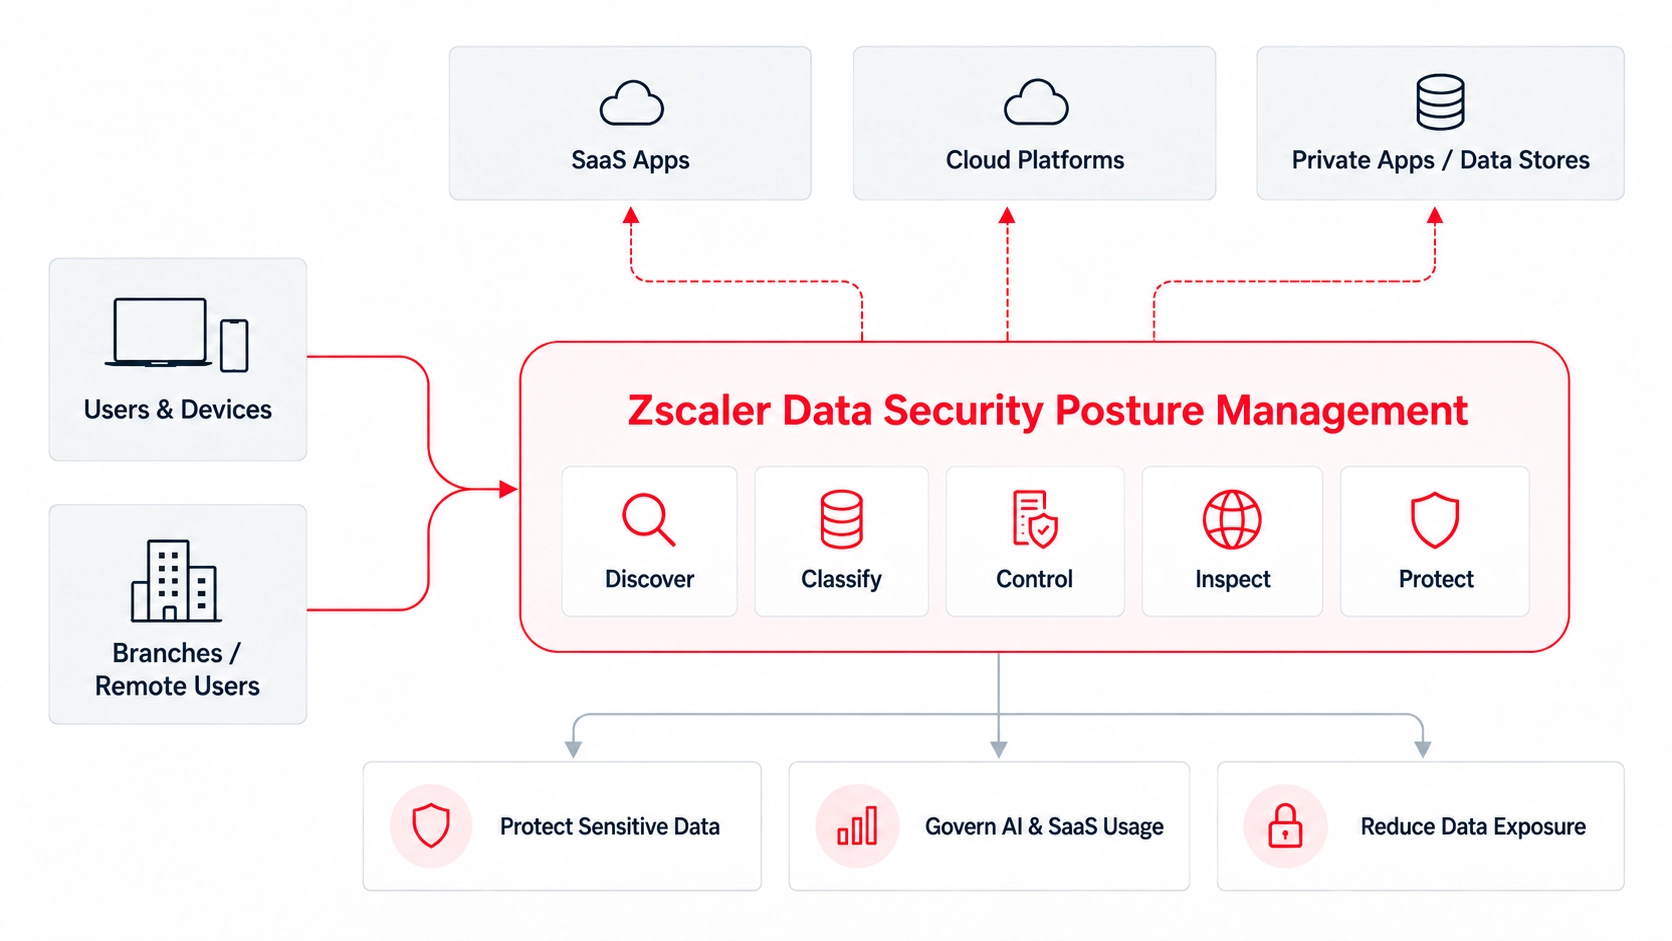
Data Security with Zscaler
Findings become actionable when security, cloud and data owners can agree on remediation priorities. Our approach connects technical discoveries to ownership, risk and practical changes rather than producing another inventory without a remediation process.
- Discover and classify sensitive data across supported cloud, SaaS and other integrated environments.
- Investigate access permissions and conditions that may expose business-critical information.
- Prioritize remediation with application and data owners.
- Track posture improvements and provide evidence for internal reviews and compliance activities.
Unified DLP: Control How Sensitive Information Is Shared
Knowing where sensitive data resides is only half the problem. Organizations also need to control how information is uploaded, downloaded, shared and transferred. Zscaler's unified DLP capabilities support consistent classification and policy enforcement across supported channels, including web, SaaS, email and endpoints, subject to product licensing and deployment.
Hararei begins by identifying meaningful data loss scenarios and aligning policy actions with the business process. Depending on sensitivity and user context, the appropriate response may be monitoring, user coaching, justification or blocking. A phased rollout helps reduce unnecessary disruption and false positives.
Web & Cloud Transfers
Inspect relevant data movement through supported web and cloud application channels and act on violations of information protection policies.
Endpoint Activity
Extend data protection to supported device activities where endpoint DLP is appropriate and enabled.
Classification & Policy
Use relevant detection methods and shared policy definitions to recognize sensitive information and apply more consistent controls.
Protect Data in SaaS & Collaboration Platforms
Collaboration platforms make enterprise information accessible across teams and organizations, but also increase the potential for accidental oversharing. Hararei can combine Zscaler's supported SaaS security and data protection capabilities to identify risky sharing, review relevant configurations and address data exposure in integrated applications.
The aim is not to prevent collaboration. It is to distinguish authorized business sharing from avoidable exposure, with policies that reflect the sensitivity of the information and the needs of employees and external partners.
Turn Security Controls Into Sustainable Governance
Technology supports data governance, but does not replace business ownership, retention decisions or organizational accountability. Hararei helps translate security requirements into measurable operating practices, including policy ownership, exception handling, incident triage, remediation tracking and reporting.
Where applicable, the resulting controls and evidence can support internal and external requirements such as privacy, industry and contractual obligations. Actual compliance depends on the wider governance program, implementation and applicable jurisdiction; deployment of a security product does not itself establish regulatory compliance.
How Hararei Helps
Assessment & Architecture
Evaluate existing DLP tools, data locations, sharing patterns and operational requirements. Identify where DSPM, DLP and SaaS security can reduce gaps or unnecessary complexity.
Deployment & Policy Design
Configure relevant Zscaler capabilities, integrate supported environments and develop practical classification and enforcement policies with business and technical stakeholders.
Legacy DLP Modernization
Review existing rules and detection methods, identify dependencies and plan a phased transition without assuming that every legacy control has a direct equivalent.
Ongoing Operations
Support policy tuning, incident workflows, reporting and periodic reviews so the deployment evolves as business requirements and risks change.
Data Protection Also Supports Secure AI Adoption
Employees and enterprise AI applications introduce another way for sensitive information to be disclosed or overshared. Data discovery, classification and DLP provide an important foundation, while AI-specific use cases require additional controls for application access, prompts and AI-related risks.
For those requirements, see Hararei's AI Security & Governance solution. The two approaches are complementary, but they address different parts of the security problem.
Contact Us Please contact Hararei for an in-depth discussion on using any of our Cloud or Cybersecurity products or services