AI Governance and LLM Security for the Enterprise
Cloud-Based AI Security with Inline Inspection, DLP & Application Controls
Enable AI Innovation Without Exposing Sensitive Data
Generative AI is becoming part of everyday enterprise work, often faster than security and governance policies can adapt. Employees may use approved assistants, coding tools and AI-enabled SaaS applications alongside unsanctioned services, creating new ways for sensitive information to leave the organization.
AI can improve productivity, accelerate decisions and transform customer experiences. The objective is to enable those benefits while controlling access, protecting information submitted to AI services and addressing threats specific to AI interactions.
Drawing on experience in regulated environments, including financial services, capital markets and global enterprise platforms, Hararei helps organizations combine Zscaler's cloud-delivered security capabilities with practical, policy-driven AI governance.
A New Class of Security Risks
AI adoption can introduce exposures that traditional application access policies do not fully address. Without adequate visibility and controls, organizations may struggle to:
- Identify which AI platforms employees are using
- Prevent confidential or regulated data from being submitted to AI services
- Enforce appropriate use of approved and unsanctioned AI applications
- Detect AI-specific threats and investigate policy violations
Blocking AI entirely is not the answer. The goal is to establish visibility and enforceable controls that support legitimate business use.
How Zscaler Helps Protect AI Adoption
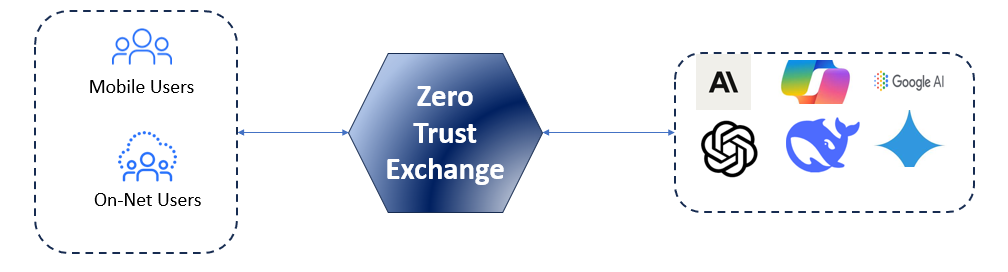
Inline inspection and policy enforcement for supported AI application traffic.
Visibility into AI Usage
Identify and categorize supported AI applications, including generative AI platforms, coding assistants and AI-enabled SaaS services. Visibility into shadow AI and usage trends helps security teams develop informed access policies.
Data Loss Prevention for AI Prompts
Apply DLP policies to supported AI interactions to detect and control the disclosure of customer information, financial records, intellectual property and other sensitive data. Depending on the configuration, policies can alert, restrict or block inappropriate submissions.
AI Access and Usage Controls
Determine which AI services users may access and how they may interact with them. Policies can distinguish approved tools from unsanctioned services and apply restrictions according to relevant user, device and application context.
Inline SSL/TLS Inspection
Because many AI applications use encrypted HTTPS traffic, inspecting eligible traffic is important for detecting sensitive data and applying policy. Zscaler supports inline inspection where enabled and permitted by the organization's inspection and privacy policies.
CASB and Browser Isolation Controls
Combine relevant inline CASB and browser isolation capabilities to manage risky interactions with supported AI and cloud applications. Depending on the application and deployment, controls can restrict uploads, downloads, clipboard activity or access from unmanaged devices.
AI Guard for AI-Specific Protection
Zscaler's AI-specific protections extend beyond application access and conventional DLP. Supported capabilities can inspect prompts and responses and apply controls addressing prompt injection, jailbreak attempts and inappropriate content, according to the deployed products and policies.
AI risks can arise during ordinary business activity, even when a user has no intention of disclosing information. Visibility into AI usage and practical controls help reduce accidental exposure while keeping approved workflows available.
Secure AI Starts with Secure Data
AI security and enterprise data security are complementary, but they address different requirements. AI security focuses on application visibility, acceptable use, prompt protection and AI-specific threats. Broader data security establishes where sensitive information resides, who can access it and how it may be shared.
Hararei's Data Security & Governance solution addresses enterprise-wide data discovery and classification, data security posture management (DSPM), data loss prevention (DLP) and SaaS data protection. These capabilities provide an important foundation for policies governing AI use without turning the AI Security solution into a general data management project.
Learn more about our Data Security & Governance solution and how it complements AI-specific controls.
A Practical Approach to Secure AI Enablement
Hararei helps organizations move from unmanaged AI adoption to policies that enable approved use while limiting unnecessary exposure:
- Discover the AI applications in use
- Identify approved AI tools and permitted use cases
- Apply appropriate protection to sensitive information entered into AI services
- Govern user actions within supported AI applications
- Address AI-specific threats where relevant protection capabilities are deployed
- Support investigations and audits with appropriate visibility and logging
Supporting Data Sovereignty and Data Protection Requirements
AI services can introduce data residency, confidentiality and accountability questions when employees submit regulated or proprietary information to external platforms. These requirements vary by jurisdiction and by the organization's data and AI use cases.
Hararei helps align AI application access, inspection and data protection policies with those requirements. Technical controls can reduce inappropriate disclosure and improve auditability, but they form only part of a wider privacy, legal and governance program.
Why Hararei
Hararei brings practical experience securing sensitive information in complex and regulated environments, including financial services, capital markets and global enterprise platforms. We understand that secure AI adoption is as much a policy and operational challenge as a technology project.
Our approach connects AI usage assessment, policy design, Zscaler deployment and operational processes. We help customers identify meaningful risks, establish controls that users can work with, and refine those controls as AI applications and business requirements change.
Advanced AI-Driven Security Architecture Deep Dive with Zscaler FAQ
Achieving next-generation, AI-enhanced protection by leveraging Zscaler's platform with the expertise of Hararei.
1. What AI-related risks does Zscaler help protect against?
Zscaler helps organizations address key risks associated with AI usage, including the unintended exposure of sensitive data through prompts, the use of unsanctioned AI applications, and interactions with potentially harmful or manipulated AI content. By inspecting traffic inline through the Zero Trust Exchange, Zscaler ensures that policies are enforced before data is transmitted to external AI platforms, reducing the likelihood of data leakage or misuse.
2. How does Zscaler prevent sensitive data from being shared with AI tools like ChatGPT?
Zscaler uses integrated Data Loss Prevention capabilities within Zscaler Internet Access to inspect user interactions with AI platforms in real time. When a user submits a prompt or uploads data, Zscaler analyzes the content for sensitive information such as personal data, financial records, or intellectual property. Based on defined policies, it can block the request, allow it with modifications, or log the activity for further review, ensuring that sensitive data is not inadvertently exposed.
3. Can Zscaler control which AI applications users are allowed to access?
Zscaler provides full visibility and control over AI application usage through its cloud access security broker functionality. It can identify AI applications being accessed across the organization and distinguish between sanctioned and unsanctioned tools. Policies can then be applied to allow access, restrict usage, or completely block certain applications, helping organizations prevent uncontrolled or risky adoption of AI services.
4. How does Zscaler protect against prompt injection or malicious AI responses?
Zscaler reduces exposure to prompt injection and malicious outputs by inspecting outbound requests and applying security policies that identify suspicious or high-risk interactions. In addition, it can leverage browser isolation to ensure that responses from AI platforms are executed in a controlled environment. This approach limits the potential impact of malicious content without requiring changes to the underlying AI models themselves.
5. Does Zscaler provide visibility into how employees are using AI tools?
Zscaler provides detailed visibility into user activity across AI platforms, allowing organizations to understand how these tools are being used in practice. This includes tracking which applications are accessed, how frequently they are used, and, depending on policy configuration, the nature of the interactions. This level of insight enables security and compliance teams to assess risk and refine governance strategies around AI adoption.
6. How does Zscaler enforce AI security policies for remote users?
Because Zscaler operates as a cloud-native platform, it applies consistent security policies regardless of where users are located. All traffic is routed through the Zero Trust Exchange, whether users are on a corporate network, at home, or traveling. This ensures that interactions with AI services are always subject to the same inspection and control mechanisms, eliminating gaps that might otherwise arise in remote or hybrid work environments.
7. Can Zscaler isolate AI sessions to prevent data leakage?
Zscaler can isolate AI sessions using its browser isolation capabilities, which execute web sessions in a secure, remote environment rather than on the user’s device. This allows organizations to tightly control how users interact with AI tools by restricting actions such as copying, pasting, downloading, or uploading data. As a result, sensitive information is prevented from being exposed either to the AI service or to the endpoint.
8. How does Zscaler support compliance requirements for AI usage?
Zscaler supports compliance efforts by enforcing data protection policies on all interactions with AI services and maintaining detailed audit logs of user activity. Organizations can define how data is handled, ensure that sensitive information is not transmitted to external platforms, and demonstrate adherence to regulatory requirements through reporting and monitoring capabilities. This enables safe and governed adoption of AI within regulated environments.
9. How does Zscaler simplify reporting and compliance for AI usage?
Zscaler simplifies reporting and compliance by providing centralized, easy-to-consume visibility into all user interactions with AI applications. Through integrated logging and analytics across the Zero Trust Exchange, organizations can quickly generate reports that show who is using AI tools, what data is being shared, and whether policies are being enforced. This allows security, risk, and compliance teams to demonstrate adherence to internal policies and external regulations without relying on multiple tools or manual data collection, significantly reducing the operational burden of governing AI usage.
Secure AI Adoption — Without Slowing the Business
Speak with Hararei about gaining visibility into AI use, protecting sensitive information in AI interactions and implementing practical, enforceable governance.
Contact Us Please contact Hararei for an in-depth discussion on using any of our Cloud or Cybersecurity products or services